Summary:
Modern marketing optimizes email for clicks, personalization, tracking, redirects, and conversions while cybersecurity teaches users to distrust many of those same behaviors. Drawing on NIST phishing research and the NIST Cybersecurity Framework 2.0, this article examines how legitimate corporate communications can inadvertently condition employees and customers to ignore phishing warning signs. The issue extends beyond security awareness into third-party risk, enterprise architecture, brand trust, and governance. Organizations need cross-functional accountability for resolving the conflict between engagement and security.
Marketing wants you to click.
Cybersecurity wants you to stop before you click.
Both are doing their jobs.
The problem begins when nobody in the enterprise has decided what should happen when those objectives collide.
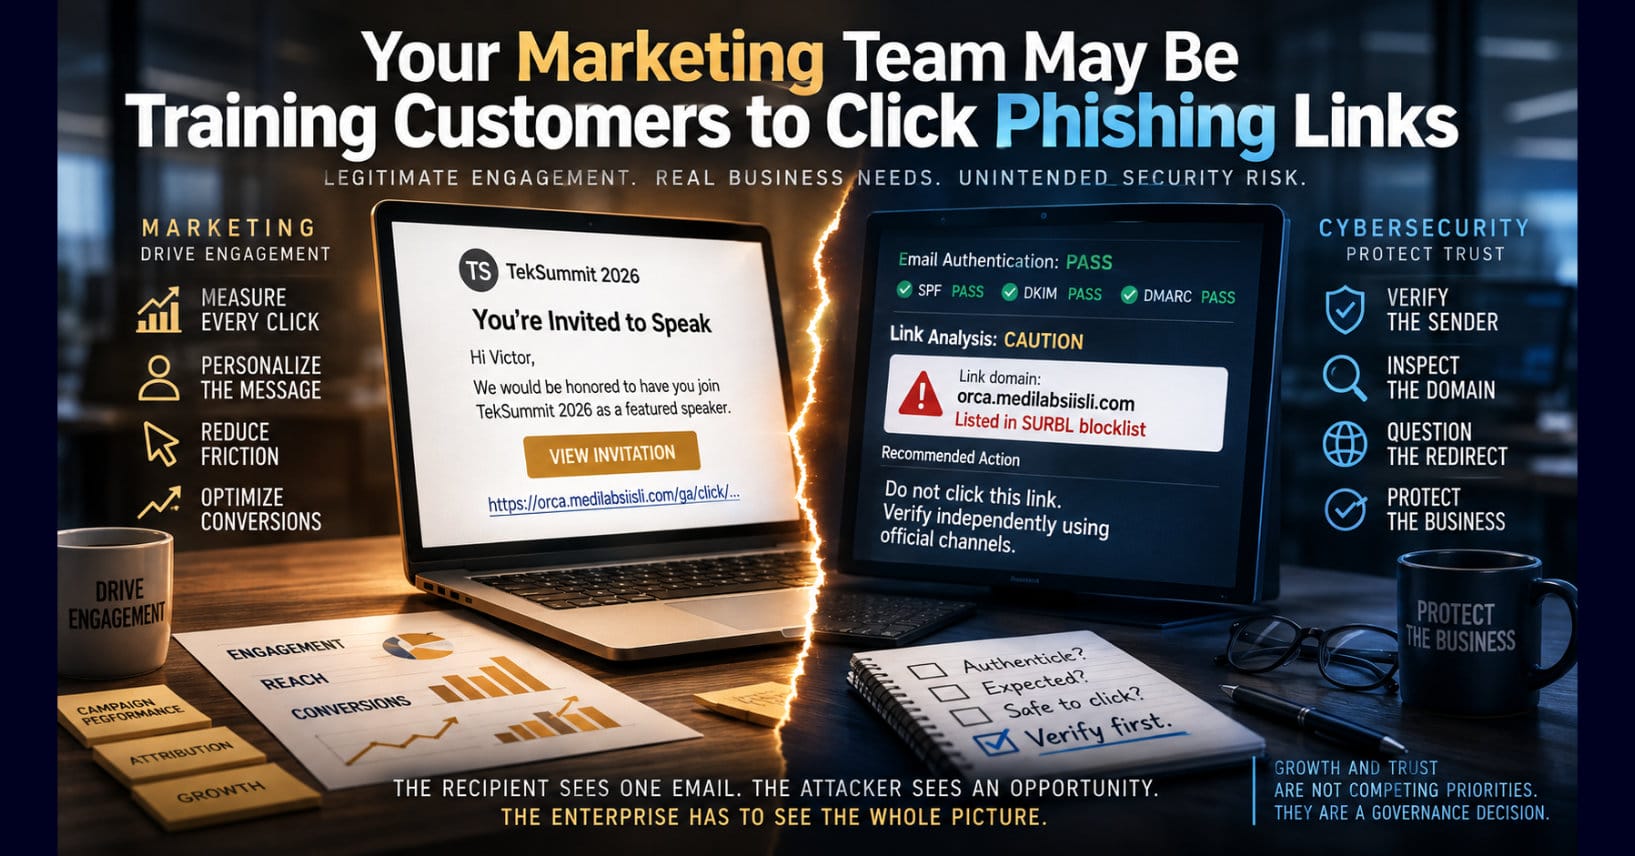
I recently received an invitation to speak at a technology summit. At first glance, the message presented several characteristics that would make a security-conscious recipient cautious. The links passed through an unfamiliar tracking domain. The domain had no obvious relationship to the organization inviting me. The message contained redirects, campaign identifiers, an open-tracking pixel, and third-party delivery infrastructure.
So I investigated it.
The organization was real.
The event was real.
SPF passed.
DKIM validated.
The email address provided for speakers could be independently verified through the organization’s legitimate web properties.
The invitation appeared to be legitimate.
And I still didn’t click the links.
That experience exposed a larger enterprise problem that has been developing for years.
We are teaching people one set of behaviors through cybersecurity awareness programs while teaching them the opposite behaviors through legitimate corporate communications.
Security Says Stop. Marketing Says Click.
Consider what employees and customers are routinely taught about phishing.
- Check the sender.
- Inspect the domain.
- Be suspicious of unexpected messages.
- Be cautious when a link goes somewhere other than where you expect.
- Do not automatically trust redirects.
- Verify unusual requests independently.
- Think before you click.
These are sensible behaviors.
Now consider how modern digital marketing works.
- Measure every click.
- Track every open.
- Personalize the subject line.
- Create urgency.
- Reduce friction.
- Use campaign-management platforms.
- Route links through analytics systems.
- Redirect users through tracking infrastructure.
- Optimize calls to action.
- Make clicking effortless.
These practices also make sense within their own discipline.
The marketing team is trying to understand engagement, attribute conversions, measure campaign performance, personalize communication, and determine what produces revenue.
The security team is trying to prevent credential theft, malware execution, social engineering, account compromise, and fraud.
The problem is not that either team is wrong.
The problem is that the recipient sees only one email.
We Are Normalizing the Warning Signs
Suppose an employee receives a legitimate benefits email containing a link routed through an unfamiliar third-party domain.
She hesitates.
Security awareness training has taught her that mismatched domains can be suspicious.
But she eventually discovers the message is legitimate.
Next week, Marketing sends a webinar invitation through another platform. Again, the visible link resolves through an unfamiliar tracking service.
Legitimate.
Then comes a customer survey.
Different redirect domain.
Legitimate.
An HR communication.
Another external platform.
Legitimate.
A conference invitation.
Another tracking domain.
Legitimate.
What has the organization taught her?
Not what the cybersecurity training intended.
It has taught her that unfamiliar domains, redirects, tracking links, and unexpected infrastructure are simply how business works.
Eventually the security warning stops functioning as a warning.
That is behavioral conditioning.
Every legitimate email that teaches a recipient to ignore a security warning makes the next phishing email easier to believe.
Attackers Do Not Need to Invent New Behavior
This is one reason phishing remains so effective.
Attackers do not necessarily need to create behavior that looks abnormal. They can imitate behavior organizations have already conditioned people to accept.
The modern employee routinely receives legitimate messages from payroll providers, benefits platforms, CRM systems, document-signing services, marketing automation systems, cloud applications, collaboration platforms, survey systems, conference platforms, recruiting systems, and dozens of other third parties.
Each introduces another domain and another trust relationship.
The recipient cannot reasonably maintain a mental inventory of all of them.
Now place a convincing phishing message into that environment.
The attacker does not have to convince the recipient that an unfamiliar domain is normal.
The enterprise has already done that.
Context Makes the Problem Harder
There is another dimension that makes this especially important.
People do not evaluate email in a vacuum.
NIST researchers Kristen Greene, Michelle Steves, Mary Theofanos, and Jennifer Kostick examined 4.5 years of workplace phishing-training data and found that an individual’s work context acts as the lens through which email cues are interpreted. People who clicked and those who did not click could notice different cues—and could interpret the same cues differently depending on how closely the premise of the message aligned with their work.
The researchers identified an especially important behavioral distinction. People who clicked were concerned about the consequences of not responding, such as failing to fulfill a work responsibility. Those who did not click were more concerned about the consequences of interacting with the message, such as downloading malware.
The researchers concluded that alignment between a person’s work context and the premise of the phishing message is a significant factor in phishing susceptibility.
That makes intuitive sense.
A CFO is more likely to pay attention to a banking or financial message.
A developer is more likely to respond to something involving source code or a repository.
A salesperson expects CRM notifications.
An HR executive expects benefits communications.
And someone who writes and speaks publicly about technology might reasonably receive an invitation to speak at a technology conference.
Context supplies credibility.
Attackers understand this.
Marketing understands it too.
That is why personalization works.
The uncomfortable reality is that the same behavioral principles that increase legitimate marketing engagement can increase the effectiveness of social engineering.
The technologies may be different.
The intentions certainly are.
But the human being receiving the message has the same brain.
Source: Greene, Kristen K., Michelle P. Steves, Mary F. Theofanos, and Jennifer A. Kostick. “User Context: An Explanatory Variable in Phishing Susceptibility.” Workshop on Usable Security (USEC), Network and Distributed Systems Security Symposium, 2018. National Institute of Standards and Technology. DOI: 10.14722/usec.2018.23016.
This Is Not a Marketing Problem
It would be easy for cybersecurity professionals to look at this situation and conclude that Marketing needs to stop using tracking technology.
That would miss the point.
Marketing has legitimate business requirements.
Executives should expect marketing leaders to measure campaign performance. They should understand which communications generate engagement, which channels produce conversions, and whether money spent on campaigns produces business results.
Removing measurement is not governance.
Nor should the CISO dictate marketing strategy.
The better question is whether the enterprise has established standards governing how customer-facing technology affects trust.
For example, must externally facing email links use domains recognizable as belonging to the organization?
Can third-party marketing platforms operate through branded subdomains?
Who evaluates the reputation of redirect infrastructure?
Who reviews changes to email delivery architecture?
What happens when a marketing provider’s domain develops a poor reputation?
Can recipients independently verify important communications?
Does the company test its own legitimate communications against the same indicators taught in security-awareness training?
Those are cross-functional questions.
And that means this is an enterprise governance problem.
NIST Cybersecurity Framework 2.0 provides an important governance foundation for this distinction. CSF 2.0 introduced GOVERN as a core function alongside IDENTIFY, PROTECT, DETECT, RESPOND, and RECOVER. The framework treats cybersecurity risk strategy, expectations, policy, roles, responsibilities, authorities, and oversight as matters that should be established, communicated, and monitored.
In other words, the conflict between Marketing’s engagement objectives and Security’s trust requirements should not be resolved accidentally by whichever technology platform happens to be deployed. Management needs defined decision rights and accountability for the resulting cyber risk.
Source: National Institute of Standards and Technology. The NIST Cybersecurity Framework (CSF) 2.0. NIST CSWP 29. February 26, 2024. DOI: 10.6028/NIST.CSWP.29.
The Third-Party Risk Nobody Calls Third-Party Risk
Organizations have become considerably more sophisticated about third-party cybersecurity risk.
Vendors undergo assessments.
Contracts contain security requirements.
Critical suppliers may receive continuous monitoring.
Cloud providers are evaluated.
Software dependencies are scrutinized.
Yet marketing technology can sometimes sit outside the way leadership conceptualizes the enterprise security boundary.
A marketing automation provider may send millions of messages representing the company’s brand.
A link-tracking provider may redirect every recipient who interacts with those messages.
An analytics provider may participate in the transaction.
A CRM may supply the recipient data.
DNS configurations may connect these services to corporate domains.
Every component participates in an external trust relationship with the customer.
That is architecture.
Whether anyone calls it architecture is irrelevant.
If a third party can influence whether your customers trust communications carrying your company’s name, that provider participates in your trust architecture.
It should be governed accordingly.
That conclusion is also consistent with NIST’s cybersecurity supply-chain guidance. CSF 2.0 includes a dedicated Cybersecurity Supply Chain Risk Management category within the GOVERN function, and NIST’s CSF 2.0 C-SCRM Quick-Start Guide calls for organizations to establish and operate a cybersecurity supply-chain risk-management capability and to define and communicate cybersecurity requirements to suppliers.
A marketing automation provider, email delivery service, analytics platform, or redirect provider may not look like a traditional “critical supplier.” But when that provider becomes part of the mechanism through which the enterprise establishes digital trust with customers, its cybersecurity posture and reputation become part of the enterprise’s risk exposure.
Source: National Institute of Standards and Technology. NIST Cybersecurity Framework 2.0: Quick-Start Guide for Cybersecurity Supply Chain Risk Management (C-SCRM). NIST SP 1305. October 2024. DOI: 10.6028/NIST.SP.1305.
Your Brand Has a Security Perimeter
Cybersecurity traditionally thinks about perimeters in technical terms: networks, identities, endpoints, applications, APIs, cloud environments.
But organizations also have a cognitive perimeter.
Customers develop expectations about what legitimate interaction with a company looks like.
What domains does it use?
What email addresses does it send from?
Where do its links go?
How does it request authentication?
How does it communicate urgent information?
How can a customer verify that a communication is genuine?
Those expectations become part of the organization’s security posture because attackers exploit them.
Brand consistency, therefore, is not merely a marketing concern.
It can become a security control.
A customer who knows that a company always directs account activity through a recognizable domain has a useful signal when something different appears.
A customer who has been exposed to ten legitimate tracking domains has far less information available when the eleventh domain appears.
The enterprise has created ambiguity.
Attackers thrive in ambiguity.
Stop Blaming the User
There is a recurring tendency in cybersecurity to place enormous responsibility on the person sitting in front of the inbox.
We send phishing simulations.
We measure click rates.
We assign additional training.
We tell people to look more carefully.
Then the enterprise itself produces communications that violate the patterns employees have been taught to distrust.
That is not a sustainable security model.
NIST’s human-centered cybersecurity research provides useful evidence for why. Its phishing research shows that susceptibility cannot be understood simply by counting who clicked. Context changes how people interpret the cues presented to them. NIST subsequently incorporated this human-context concept into its Phish Scale research, which is designed to help organizations assess the difficulty of detecting particular phishing messages rather than treating all phishing exercises as equivalent measures of user performance.
That changes the governance question.
Instead of asking only, “Why did the employee click?” leadership should also ask, “What environment did we design around that decision?”
If we want people to make better security decisions, we need to design environments in which the safe decision is also the understandable decision.
The employee should not need to become a DNS analyst.
The customer should not need to inspect email headers.
The executive should not need to investigate five domains before determining whether a speaking invitation is legitimate.
Good architecture reduces the amount of trust the human being is required to manufacture.
Sources: Greene et al., “User Context: An Explanatory Variable in Phishing Susceptibility,” NIST, 2018; Dawkins, Shanee, and Jody Jacobs, “Phishing for User Context: Understanding the NIST Phish Scale,” NIST, 2023.
Security Awareness Should Apply to the Sender Too
Perhaps organizations need to reverse the traditional security-awareness exercise.
Instead of asking only:
“Would our employees click this simulated phishing email?”
Ask:
“Would our legitimate email pass our own phishing test?”
Take actual messages produced by Marketing, HR, Finance, Recruiting, Sales, and other functions.
Examine them using the organization’s own security-awareness criteria.
Does the sender identity make sense?
Are the domains recognizable?
Do links unexpectedly redirect?
Does the message manufacture unnecessary urgency?
Is the recipient asked to authenticate after following an emailed link?
Can the communication be independently verified?
Would your security team tell an employee to click it?
That last question could produce some uncomfortable meetings.
Those meetings would probably be useful.
NIST CSF 2.0 reinforces the need for cybersecurity awareness and training while placing governance above the operational cybersecurity functions. Taken together, those concepts suggest something important: awareness cannot be treated solely as a responsibility imposed on users. The enterprise also has to govern the environment in which those users are expected to make security decisions.
Someone Has to Own the Collision
The organizational structure makes this problem predictable.
- Marketing owns engagement.
- Security owns cyber risk.
- IT may own DNS and messaging infrastructure.
- Procurement owns vendor relationships.
- Legal owns contractual and privacy considerations.
- Compliance may own regulatory requirements.
- Customer Experience owns friction.
- Communications owns brand consistency.
Everyone owns part of the problem.
Which often means nobody owns the outcome.
That is where governance matters.
NIST CSF 2.0 explicitly elevates governance into the cybersecurity risk-management lifecycle. Its GOVERN function is intended to establish and monitor cybersecurity risk-management strategy, expectations, and policy and to inform how the other five functions are implemented.
Governance does not require the board to approve tracking URLs.
It requires leadership to establish decision rights, accountability, standards, and escalation paths when legitimate enterprise objectives conflict.
Marketing should not have to guess what constitutes an acceptable trust architecture.
Security should not discover new externally facing communication infrastructure after deployment.
IT should not be forced to reconcile conflicting requirements without an accountable business owner.
And customers should not become the integration layer between all three.
Governance reference: National Institute of Standards and Technology. The NIST Cybersecurity Framework (CSF) 2.0. NIST CSWP 29, 2024.
Design Communications Worthy of Trust
The goal should not be to eliminate modern marketing technology.
It should be to make legitimate communication distinguishable from malicious communication wherever reasonably possible.
Use recognizable domains.
Minimize unnecessary redirect chains.
Prefer branded infrastructure where practical.
Monitor the reputation of domains representing the organization.
Reduce avoidable third-party dependencies.
Provide independent verification paths for consequential communications.
Align security-awareness guidance with actual corporate communication practices.
And when measurement conflicts with trust, make the tradeoff explicitly rather than allowing technology defaults to make the decision.
This is not merely about email.
It is about whether the enterprise presents a coherent trust model to the people interacting with it.
The Enterprise Takeaway
Marketing wants people to click.
Cybersecurity wants people to stop and think before they click.
Both are reasonable objectives.
But an organization cannot spend Monday teaching employees that unfamiliar links are dangerous and Tuesday sending legitimate communications that require them to ignore that lesson.
Eventually people learn which behavior the organization actually rewards.
That is the part leadership should care about.
The next successful phishing attack may not work because an employee forgot the security-awareness training.
It may work because years of legitimate corporate communications taught that employee when to ignore it.
References
Greene, Kristen K., Michelle P. Steves, Mary F. Theofanos, and Jennifer A. Kostick. “User Context: An Explanatory Variable in Phishing Susceptibility.” Workshop on Usable Security (USEC), Network and Distributed Systems Security Symposium, 2018. National Institute of Standards and Technology. The study analyzed 4.5 years of workplace phishing exercises and found that work context significantly affects how users interpret phishing cues.
NIST CSRC — User Context: An Explanatory Variable in Phishing Susceptibility
Dawkins, Shanee, and Jody Jacobs. “Phishing for User Context: Understanding the NIST Phish Scale.” Federal Information Security Educators (FISSEA) Summer Virtual Forum 2023. National Institute of Standards and Technology, August 23, 2023. The presentation explains how user context contributes to phishing-detection difficulty and the development and application of the NIST Phish Scale.
NIST — Phishing for User Context: Understanding the NIST Phish Scale
Pascoe, Cherilyn, Stephen Quinn, and Karen Scarfone. The NIST Cybersecurity Framework (CSF) 2.0. NIST CSWP 29. National Institute of Standards and Technology, February 26, 2024. CSF 2.0 establishes GOVERN as a core cybersecurity function and addresses cybersecurity risk governance, roles, responsibilities, authorities, policy, and supply-chain risk.
NIST CSRC — The NIST Cybersecurity Framework (CSF) 2.0
Boyens, Jon M., Rebecca McWhite, Laura Calloway, Nadya Bartol, and Karen Scarfone. NIST Cybersecurity Framework 2.0: Quick-Start Guide for Cybersecurity Supply Chain Risk Management (C-SCRM). NIST SP 1305. National Institute of Standards and Technology, October 21, 2024. The guide specifically addresses using CSF 2.0’s GV.SC category to establish C-SCRM capabilities and define cybersecurity requirements for suppliers.
NIST CSRC — CSF 2.0 Quick-Start Guide for Cybersecurity Supply Chain Risk Management